The product, on the risk surface

AIState Risk™

One platform for the entire risk surface.

Compliance, AML, Fraud and Cyber are one problem seen from four desks: the same customers, the same counterparties, the same devices and accounts, split across systems that do not agree. AIState Risk reads those systems where they live, resolves them into one knowledge graph, and gives each desk its own reading of the same facts — with agencies doing the work and approval wherever your authority matrix reserves the decision.

ONE ESTATE · ONE RESOLVED GRAPH · RECORDED ON THE RUNNING PLATFORM

From a demonstration on the live platform with an illustrative bank and illustrative data — see the day.

ComplianceScreening, alert disposition, KYC refresh, regulatory reporting — every decision carrying its source and policy version.
AMLMule networks, layering and structuring across accounts, counterparties and chains — patterns, not single alerts.
FraudAccount takeover, scam and payment fraud: exposure, device, session and money in one picture, with recovery actions.
CyberIndicators and sightings, infrastructure pivots, intrusion timelines and attribution — on the same graph as the customers affected.
COMPLIANCE
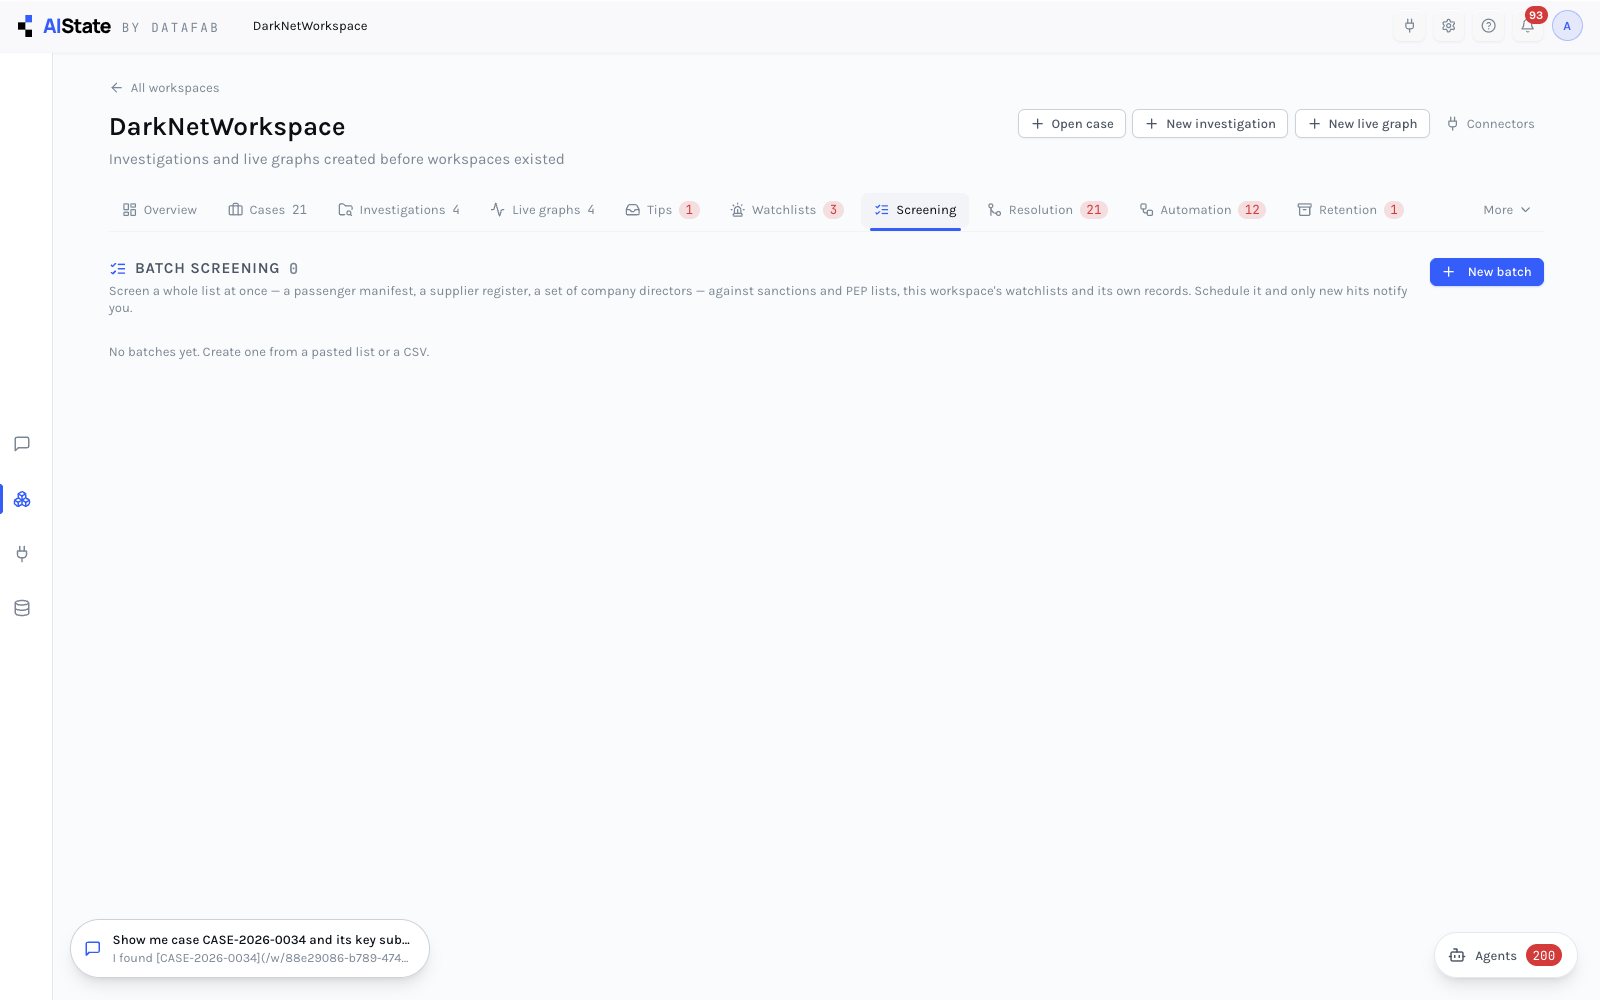
A screening batch with its hits and decisions
Screening, with the policy that firedSanctions, watchlists and your own entities in one pass; each run diffed against the last.
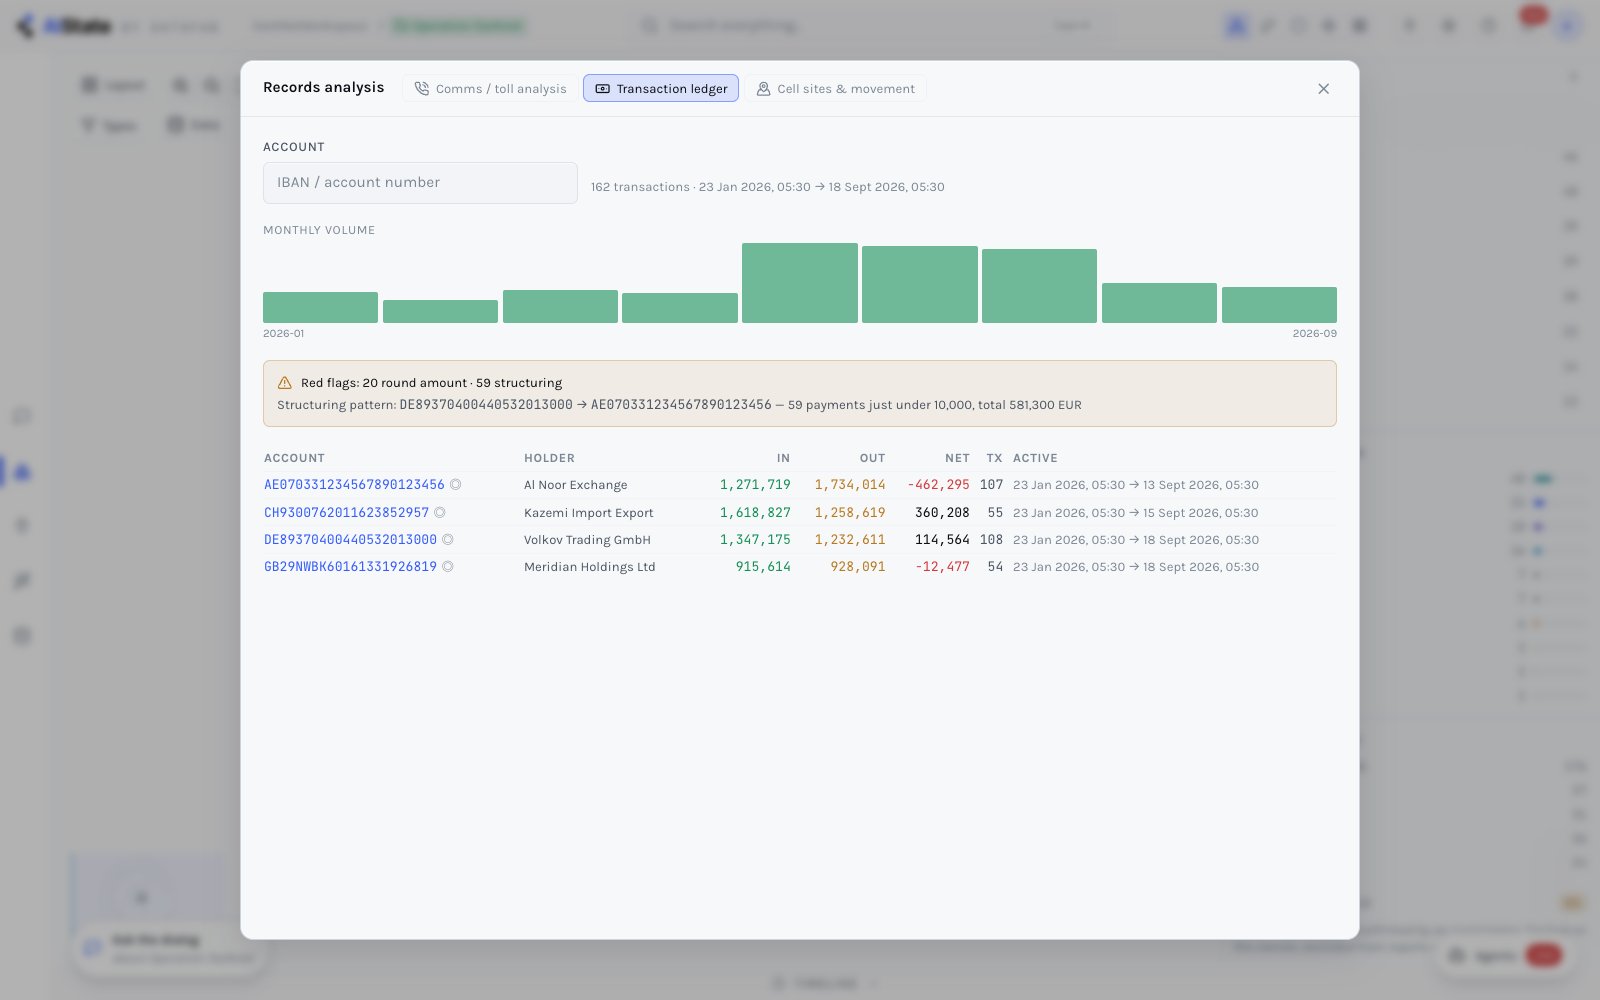
AML
A transaction ledger with counterparties and flags
Money, as a patternPer-account flows, counterparties and structuring flags across ledgers, statements and payment records.
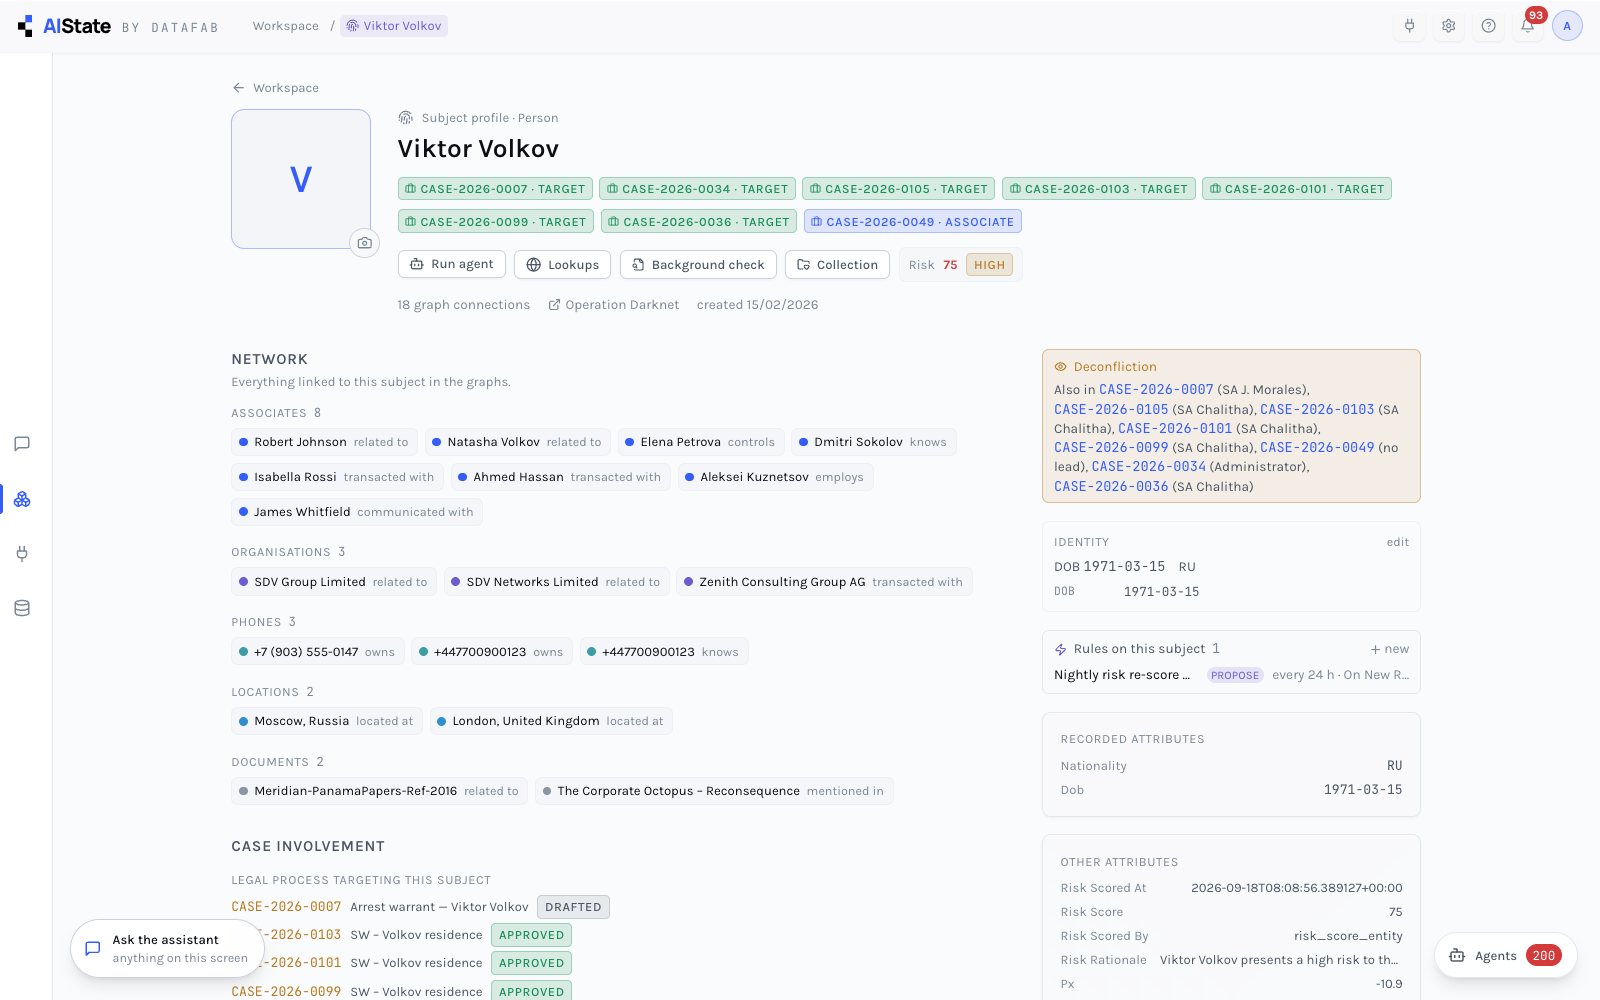
FRAUD
A subject profile with identifiers and linked records
One subject, every contextIdentifiers, devices, accounts and the cases a person already appears in — resolved once.
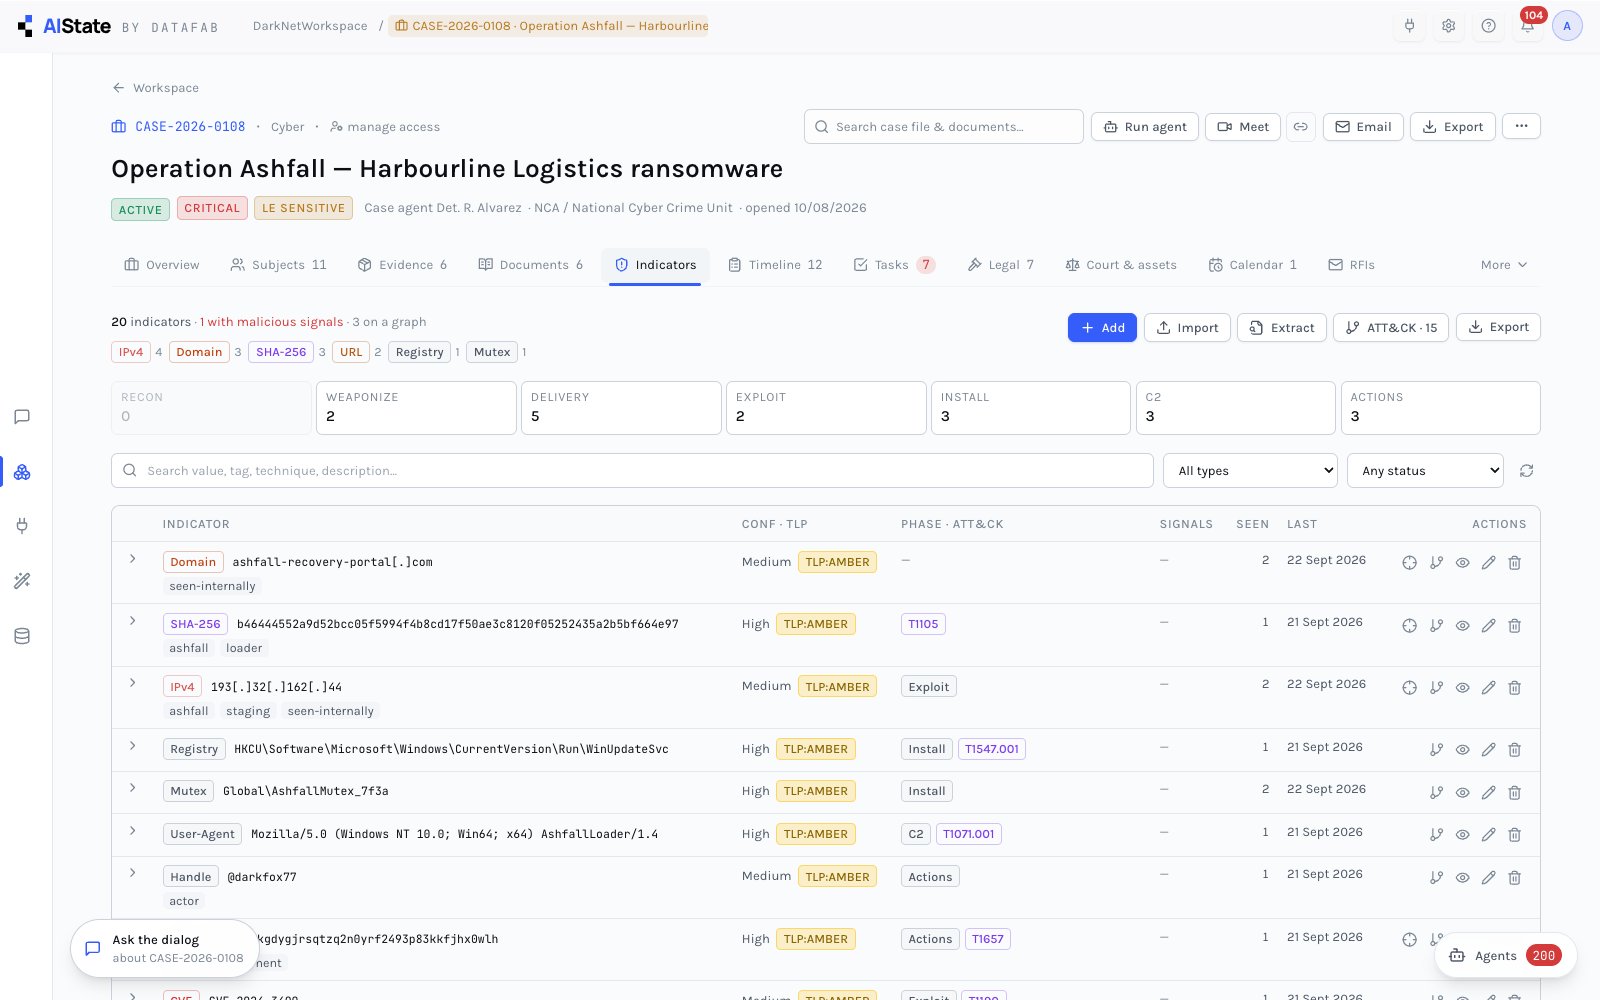
CYBER
An indicator register with kill chain and ATT&CK mapping
Indicators on the same graphKill chain and ATT&CK against the customers, accounts and devices actually affected.

Same customer. Different context. Same asset — each function reads the resolved entity through the lens its purpose requires, while provenance and governance stay underneath all of them.
What it does

Detect, triage, investigate, act — and be able to show why.

The work of a risk function is a loop. AIState Risk runs the whole loop on one graph, rather than handing it between a monitoring tool, a case tool and a spreadsheet.

DETECT · WATCHES
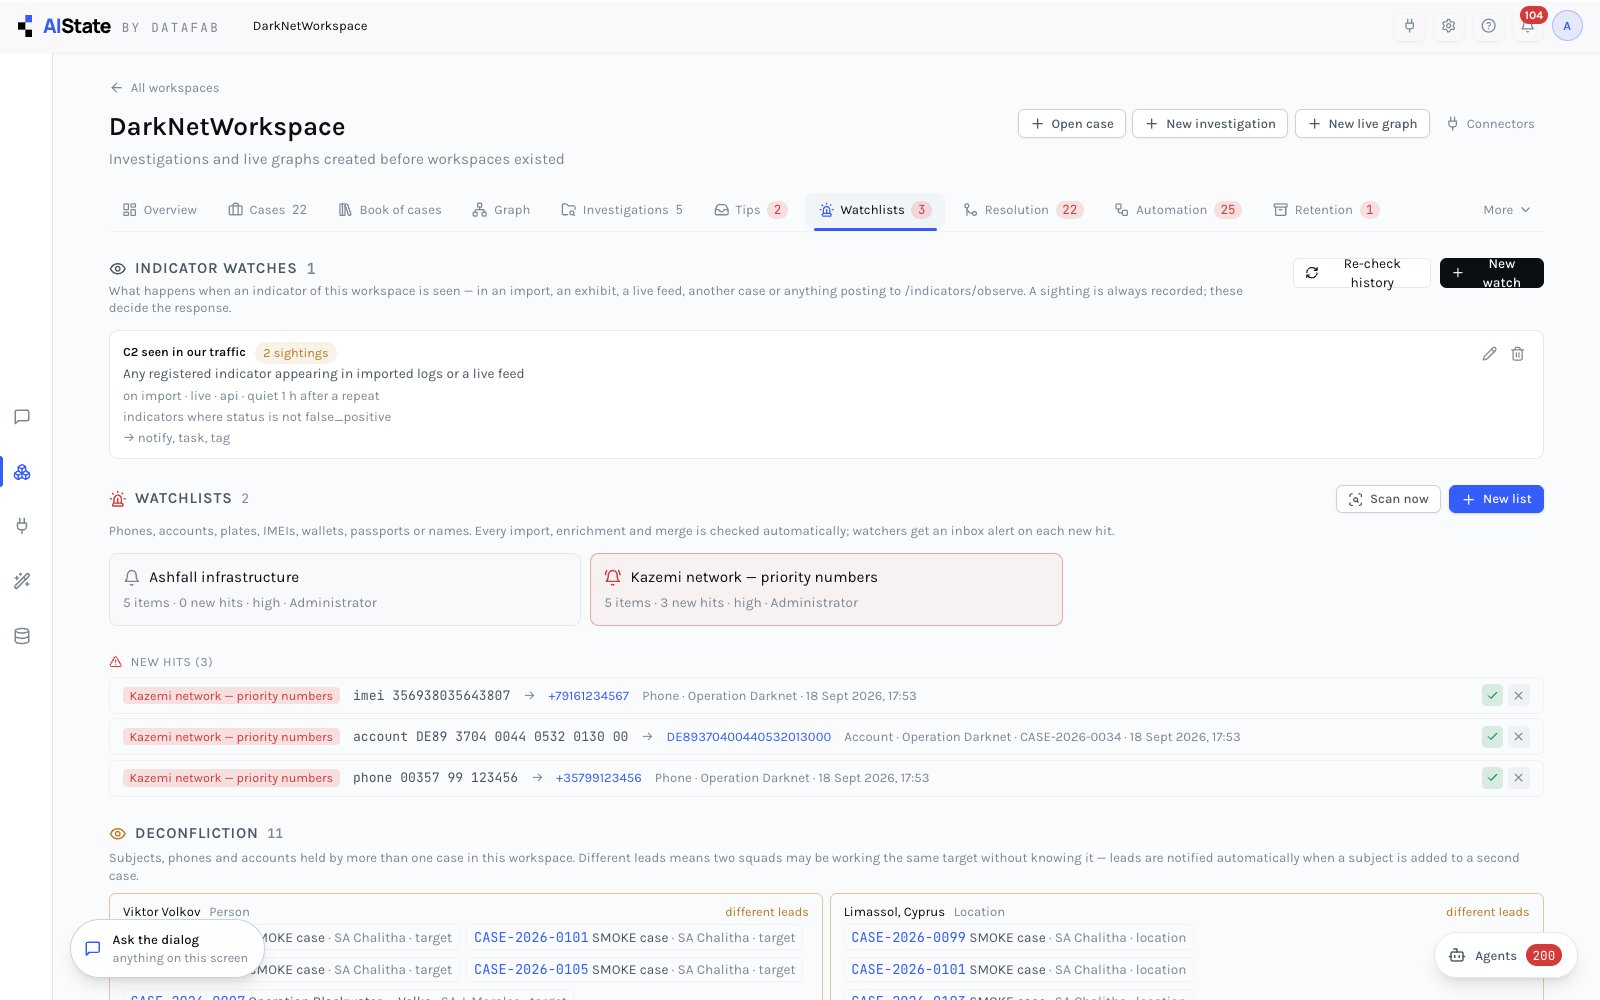
Indicator watches with their conditions and actions
A watch is policy you writeSources, scope, condition and the actions that follow — nothing about the response is hard-coded.
INVESTIGATE · AGENCY RUN
Every run shows its workingContext, model calls, each tool and what it wrote — on the server clock, kept with the result.
ACT · REPORT
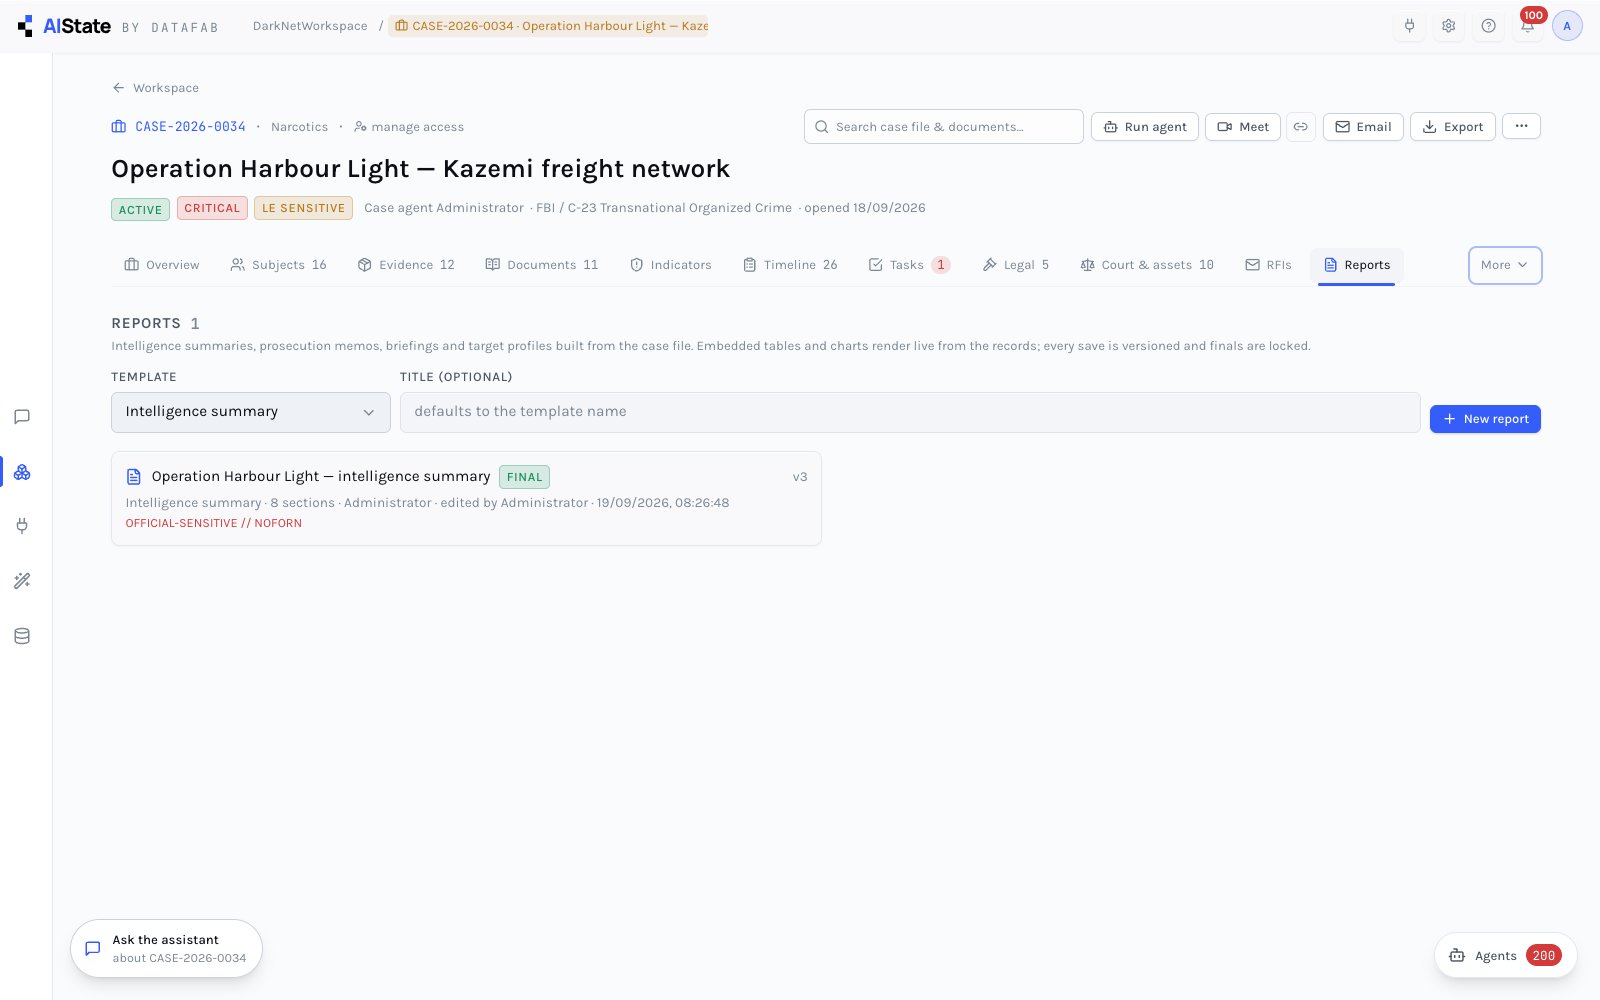
A case report being assembled from the case file
The product at the endReports built from the case file itself, versioned and locked when they are finalised.
Why it is different

Not another tool beside the others — the layer that makes them one estate.

No migration

Your systems stay where they are

Read in place over named, read-only connections. Nothing is copied into a vendor store, and the systems of record keep their owners.

weeks, not quarters
One graph

Flat rows become multi-dimensional

The same customer, account, device or wallet is one object wherever it was read from, carrying its relationships — explicit and inferred — rather than waiting for a join.

resolve once · use many times
Agency, governed

Agencies do the work; people keep the decisions you reserve

Agencies are configuration your own people compose. Every effect is declared in advance, and waits only where your authority matrix reserves the approval; every run keeps its trace — and the autonomy dial is yours to set.

L0 deterministic → L4 where policy allows
Defensible

The answer carries its basis

Every value keeps its source, citation and confidence; every decision its policy version; every case a hash-chained trail. A regulator can replay it.

assessed against NIST 800-53 on every load
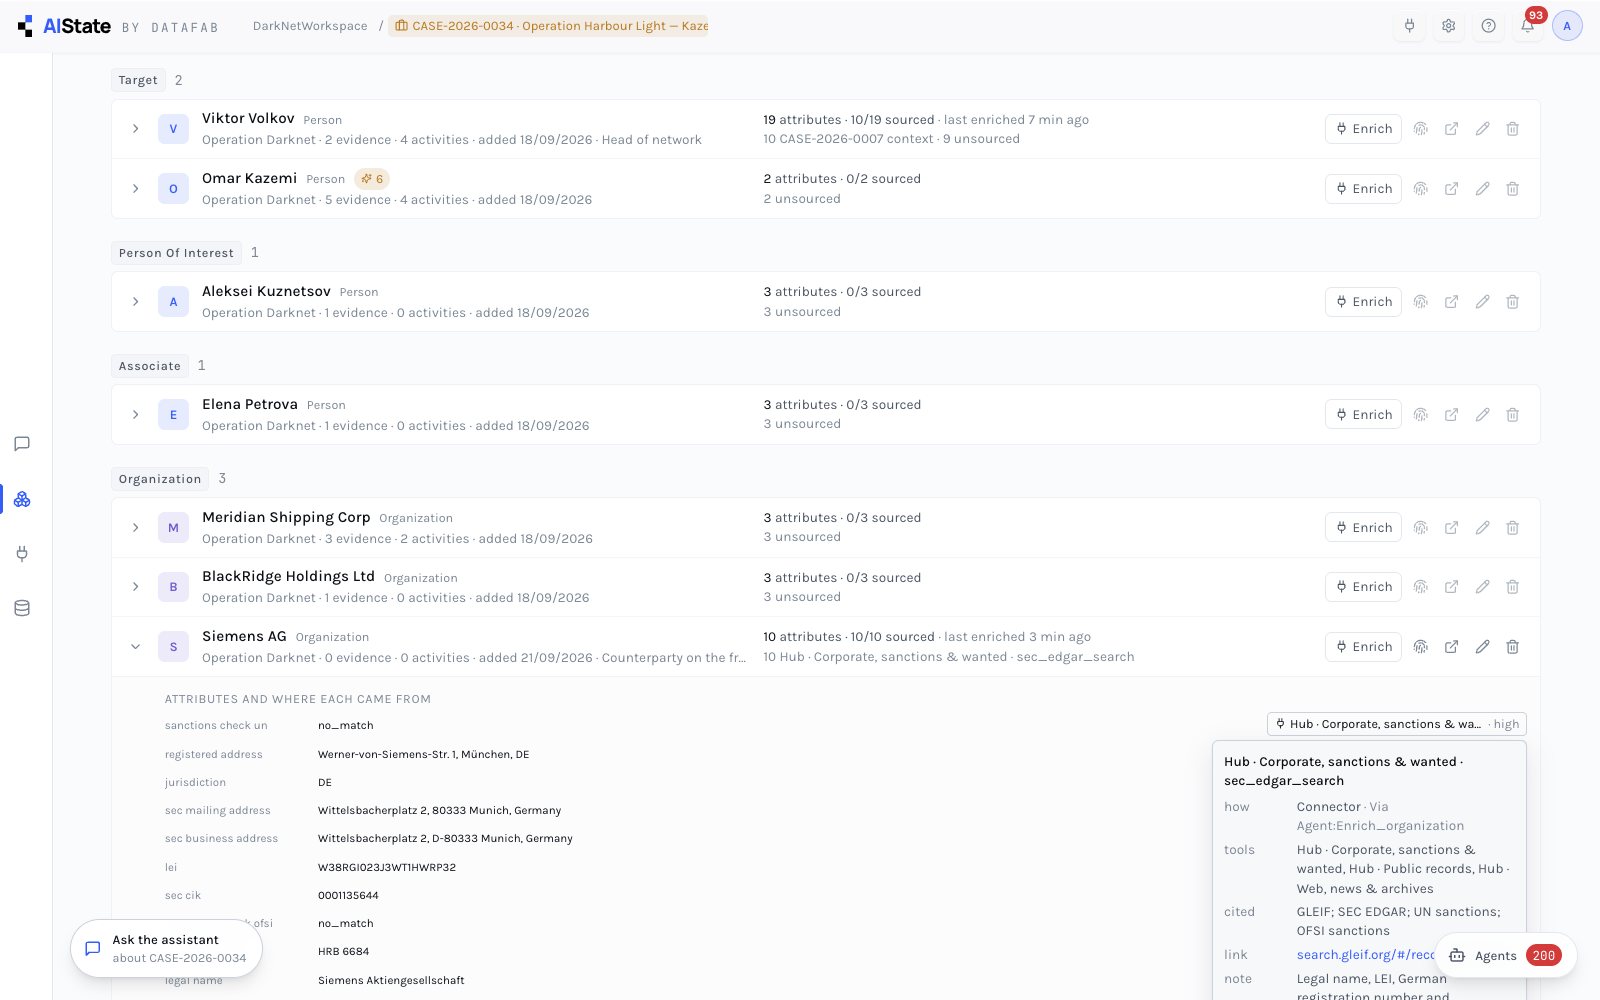
PROVENANCE · PER ATTRIBUTE
Attribute provenance showing where each value came from
Where every value came fromConnector, tool, citation, confidence and who wrote it — per attribute, with the values it replaced.
AUDIT · HASH-CHAINED
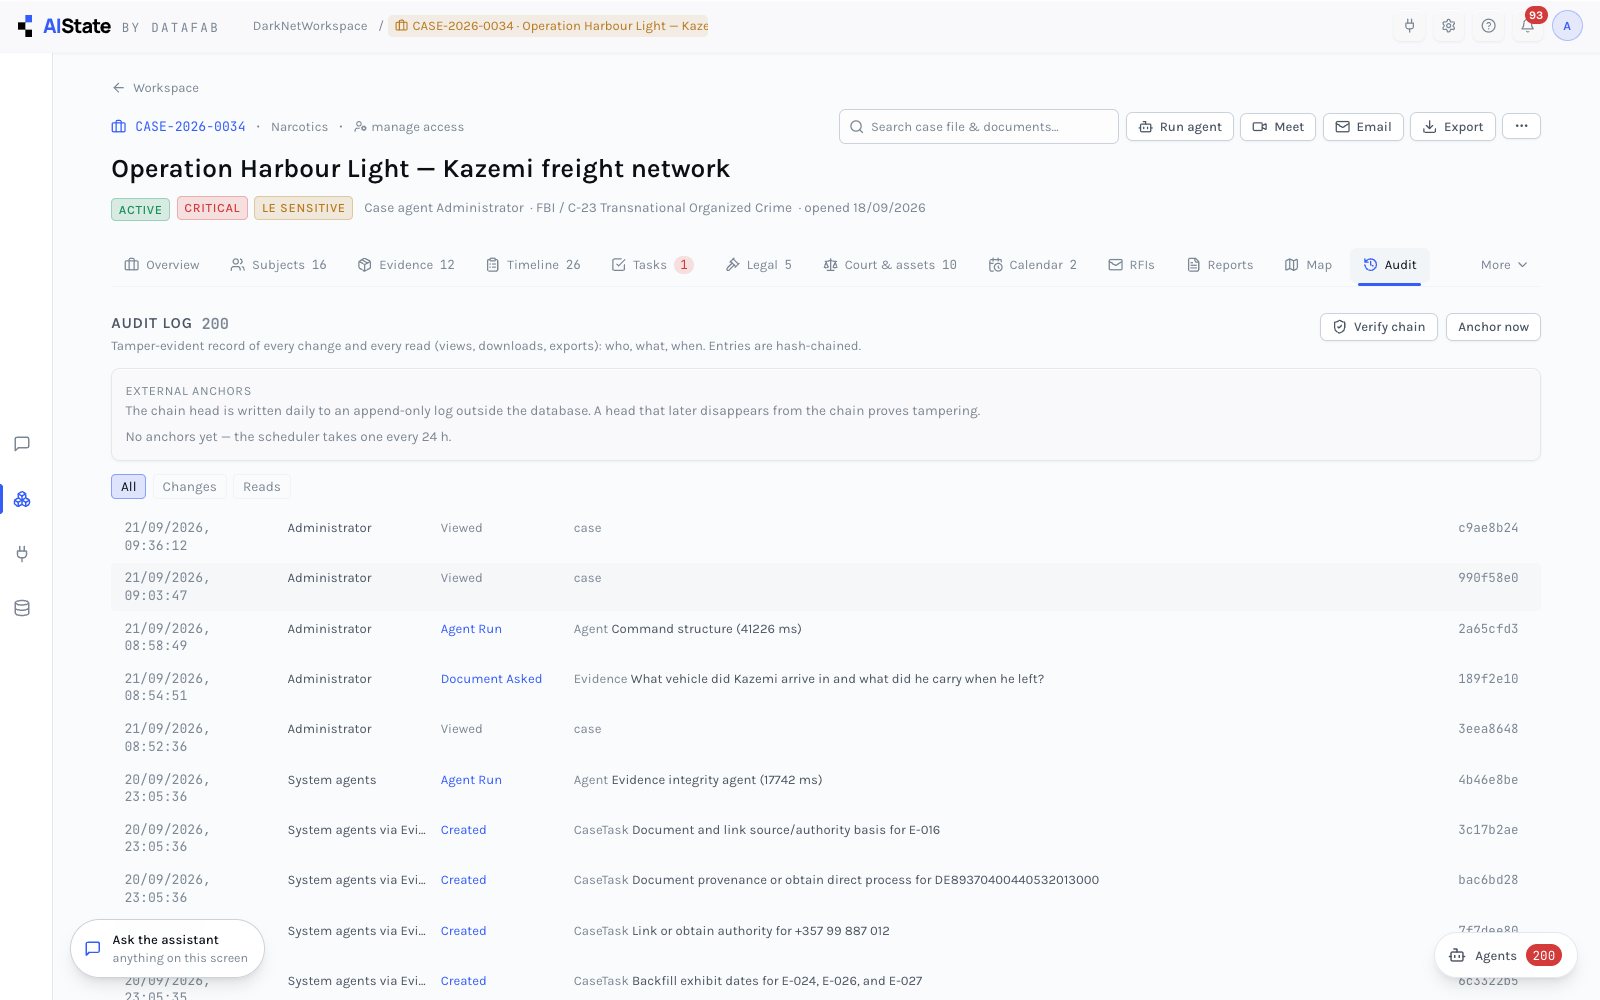
A case audit trail with chain verification
A trail that can be replayedEvery mutation and every read, hash-chained per case and anchored daily — verifiable on demand.

What accumulates is yours — the thesis →

Watch it work

A cyber-fraud case, end to end on the live system.

Narrated, unedited, on the running platform: indicators and sightings, the resolved graph, the agencies that do the reading, and the case that comes out of it.

All narrated use cases →

Lifecycle cost

Lower cost across the whole life of the platform.

Each stage against market-standard cost.

  1. Bring it in

    40–50% lower

    Weeks, not quarters — read in place, with no migration programme.

  2. Build and extract

    75–85% lower

    Your people and your partner compose it. No standing team of vendor engineers.

  3. Run it

    45–65% lower

    Depending on volume — the agencies carry the work, people take the decisions.

  4. Leave it

    90% lower

    Systems of record were never touched. Export the identity layer, policy, decisions and audit trail.

Illustrative. Run reduction varies with volume; every figure is validated against your own estate in the proof of value.

Where it runs

A utility per domain, on one platform.

AIState Risk™ · AIState Compliance™ · AIState Real Estate™. The domain lives in the ontology, the logic, the processes, the sources and the semantic context — authored as configuration, not built as new code.

The platform every product inherits →